Governance

View of a building of the Miltenyi Biotec headquarter campus in Bergisch Gladbach, Rhineland, Germany, with one icon (governance) on violet background
Logo

Governance

Ethical leadership, transparent operations, responsible partnerships

We believe that doing science responsibly starts with doing business responsibly. That means staying true to our values – acting with integrity, treating people fairly, and respecting human rights in everything we do. Our approach to governance helps us make thoughtful decisions, stay accountable, and build trust across our teams and with our partners.

Compliance – standards that guide us

Our corporate governance policies set clear expectations for how we work. They define our ethical standards, guide compliance, and reflect our commitment to responsible business practices wherever we operate.

We uphold a strict zero-tolerance policy toward all forms of corruption, including bribery, fraud, and extortion. Our global anti-corruption policy applies to all employees, directors, contractors, and agents.

Core principles include:

  • Prohibition of bribery and the acceptance of improper gifts
  • Mandatory due diligence for all third-party relationships
  • Clear guidelines on conflicts of interest
  • Robust training programs and accessible reporting channels to promote awareness and ensure compliance

Any violation of this policy may lead to disciplinary action and legal consequences. Through these measures, we protect our integrity, reputation, and shared values at every level of our organization.

Policies and guidelines

Explore our environment, social, and governance policies and guidelines to see the positive impact we’re making. All documents can be downloaded.

Learn more

Bioethical principles

At Miltenyi Biotec, we see the immense potential of human pluripotent stem cells, especially induced pluripotent stem cells (iPSCs), to drive progress in regenerative medicine, drug development, and disease modeling.

We promote the ethical and responsible use of these cells by applying advanced technologies and working closely with the scientific community. While basic research involving human embryonic stem cells (ESCs) is conducted under strict ethical and legal oversight, our primary focus is on iPSCs, which are derived from adult cells such as blood or skin. This approach enables scientific progress while ensuring full donor consent.

Applications and ethical oversight

Miltenyi Biotec supports the scientific community with tools and platforms for stem cell research. While we do not use human stem cells in therapies ourselves, we provide enabling technologies to support those who do.

Areas of support:

  • Regenerative medicine: We facilitate the development of cell-based therapies through platforms like the CliniMACS Prodigy®, a GMP-compliant system for automated stem cell processing.
  • Disease modeling and drug testing: Our technologies help create physiologically relevant human cell models, enabling more predictive and ethical preclinical testing.

Miltenyi Biotec’s guiding principles for pluripotent stem cell research

  • Ethical sourcing and donor consent: All cells are sourced ethically, with fully informed donor consent, especially in the case of iPSCs. Research involving human embryonic stem cells is conducted only under strict ethical and legal oversight.

  • Scientific integrity and innovation: We support scientific progress through reproducible, high-quality technologies that enable research on iPSCs and other ethically sourced cells.

  • Patient safety and responsibility: Although Miltenyi Biotec does not apply therapies directly, our platforms help developers ensure safety and efficacy throughout preclinical and clinical development.

  • Regulatory compliance and transparency: We follow international regulations and bioethical standards, maintaining open and transparent communication with stakeholders and regulatory bodies.

  • Ethical boundaries in embryonic research: We do not commercialize human embryos or embryo-derived cells.

  • Advancement of regenerative medicine: Our technologies contribute to the development of innovative treatments for conditions such as neurodegenerative, cardiovascular, and immune-related diseases.

  • Sustainability and social responsibility: Ethical sourcing, responsible production, and environmental sustainability are integrated into all aspects of our research support and operations.

Supplier management

Miltenyi Biotec integrates sustainability into procurement practices to support long-term value creation, regulatory alignment, and shared progress. Drawing on internationally recognized frameworks such as the International Labour Organization (ILO), the German Supply Chain Due Diligence Act (LkSG), and the EU Corporate Sustainability Reporting Directive (CSRD), we aim to foster a resilient and responsible supply chain aligned with our prioritized Sustainable Development Goals (SDGs).
3 – Good health and well-being

We are forward-thinking and contribute to a healthier future.
5 – Gender equality

We stand for equality across genders, as well as for the empowerment of women.
8 – Decent work and economic growth

We support equal access to education and enable life-long learning.
12 – Responsible consumption and production

We believe that sustainability and innovation go hand-in-hand.
13 – Climate action

We make a meaningful, lasting impact in the communities in which we operate.

Through ongoing monitoring, assessment, and disclosure of relevant sustainability data, we seek to identify and address risks early, enhance transparency, and promote accountability across our supplier network.

Our supplier code of conduct outlines the ethical, social, and environmental standards we expect from all partners. It is built on key principles, including:

  • Prohibition of child, forced, and slave labor
  • Fair wages, non-discrimination, and occupational safety
  • Environmental stewardship and climate action
  • Protection of land rights and responsible sourcing

Suppliers are required to uphold these standards not only within their own operations but also across their entire supply chain. Non-compliance may result in corrective actions or, in severe cases, termination of the business relationship.

You can find the code of conduct in our download section.

Security, Risk & Compliance

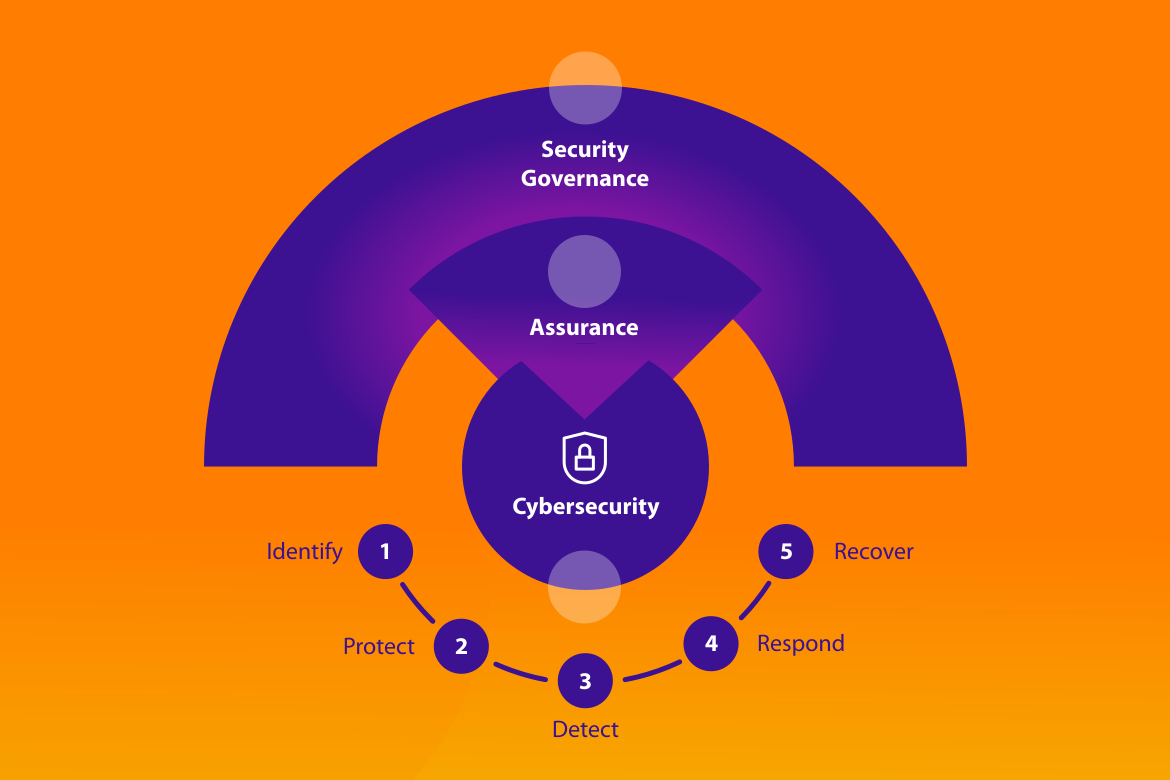
Security, Risk & Compliance consists of three departments: Security Governance, Assurance and Cybersecurity.

Security Governance

Security Governance secures Miltenyi Group's information globally through a risk-based approach. This helps us to maintain accountability, transparency, and alignment with both our internal rules and external laws, regulations and guidelines.

Security Governance

Security Governance secures Miltenyi Group's information globally through a risk-based approach. This helps us to maintain accountability, transparency, and alignment with both our internal rules and external laws, regulations and guidelines.

Assurance

Assurance acts as a safety net, enabling our operations to always run smoothly. Through audits, risk management, and compliance checks, it enforces rules, controls risks, and makes sure our cybersecurity is state of the art.

Assurance

Assurance acts as a safety net, enabling our operations to always run smoothly. Through audits, risk management, and compliance checks, it enforces rules, controls risks, and makes sure our cybersecurity is state of the art.

Cybersecurity

The main goal of our Cybersecurity team is to safeguard our data, systems and networks, from cyber threats. It follows a five-step approach (Identify → Protect → Detect → Respond → Recover) to ensure maximum security.

Cybersecurity

The main goal of our Cybersecurity team is to safeguard our data, systems and networks, from cyber threats. It follows a five-step approach (Identify → Protect → Detect → Respond → Recover) to ensure maximum security.

Security Governance

Security Governance secures Miltenyi Group's information globally through a risk-based approach. This helps us to maintain accountability, transparency, and alignment with both our internal rules and external laws, regulations and guidelines.

Security Governance

Security Governance secures Miltenyi Group's information globally through a risk-based approach. This helps us to maintain accountability, transparency, and alignment with both our internal rules and external laws, regulations and guidelines.

Assurance

Assurance acts as a safety net, enabling our operations to always run smoothly. Through audits, risk management, and compliance checks, it enforces rules, controls risks, and makes sure our cybersecurity is state of the art.

Assurance

Assurance acts as a safety net, enabling our operations to always run smoothly. Through audits, risk management, and compliance checks, it enforces rules, controls risks, and makes sure our cybersecurity is state of the art.

Cybersecurity

The main goal of our Cybersecurity team is to safeguard our data, systems and networks, from cyber threats. It follows a five-step approach (Identify → Protect → Detect → Respond → Recover) to ensure maximum security.

Cybersecurity

The main goal of our Cybersecurity team is to safeguard our data, systems and networks, from cyber threats. It follows a five-step approach (Identify → Protect → Detect → Respond → Recover) to ensure maximum security.

Information security and the biomedical Industry

For over 36 years, the Miltenyi Group has played a key role in advancing biomedical research and enabling cell and gene therapy.

The sensitive nature of biomedical data, including patient related records, research findings, and proprietary technologies, makes us a prime target for cybercriminals.

Ensuring robust information security is not just a technical necessity but a moral imperative. By prioritizing data protection, the Miltenyi Group safeguards patient privacy, protects valuable research, ensures regulatory compliance, mitigates operational risks, and builds public trust.

The Board of Management holds overall accountability for ensuring strong Information Security policies, balancing risks, and compliance needs.

The Chief Information Security Officer manages Information Security for the whole Miltenyi Group with a strong infrastructure.
Framework and standards

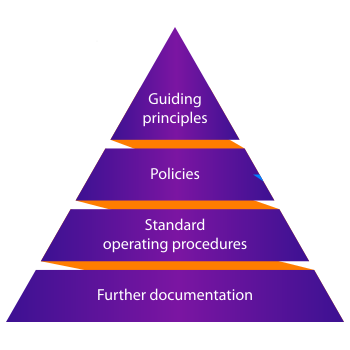
Our policy framework is in accordance with international standards, such as ISO 27001:2022, ISA/IEC-62443, and NIST 800.

Additionally, we are aligned with the German BSI-Grundschutz to ensure reliable information security.

The framework is subject to continual evaluation and enhancement to ensure compliance with global legal and regulatory requirements.

As we continue to evolve, so does our commitment to
robust and adaptive information security measures.

You have previously chosen International as your location.
What do you want to do?